Feature
Secure & tokenize payments. Keep card data off your servers.
Collect payment details through Orchestra’s secure form, store them in Orchestra’s vault, and use a token in supported payment flows.
Data boundary
Raw card data stops before your server.
The secure payment form sends card data directly to Orchestra. Your application receives only a token, helping reduce your PCI DSS scope.
Token storage
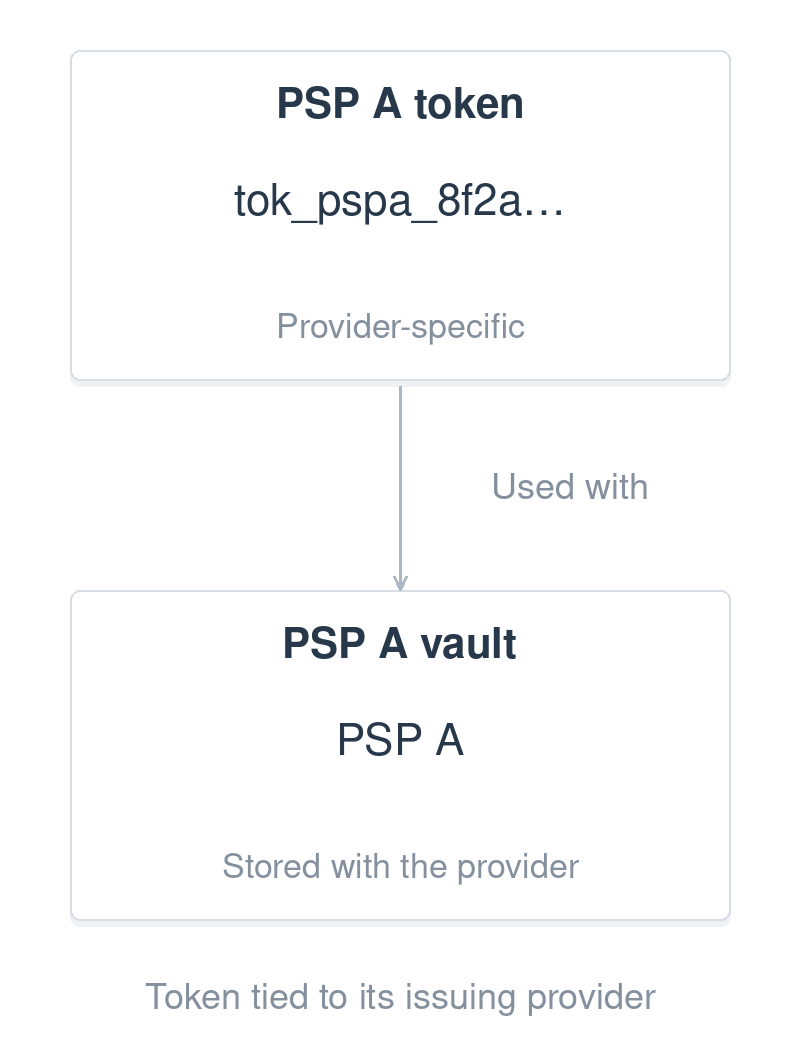
Choose where the token lives.
The vault determines where the token can be used.
Orchestra vault
- One Orchestra token
- Use across supported PSP connections
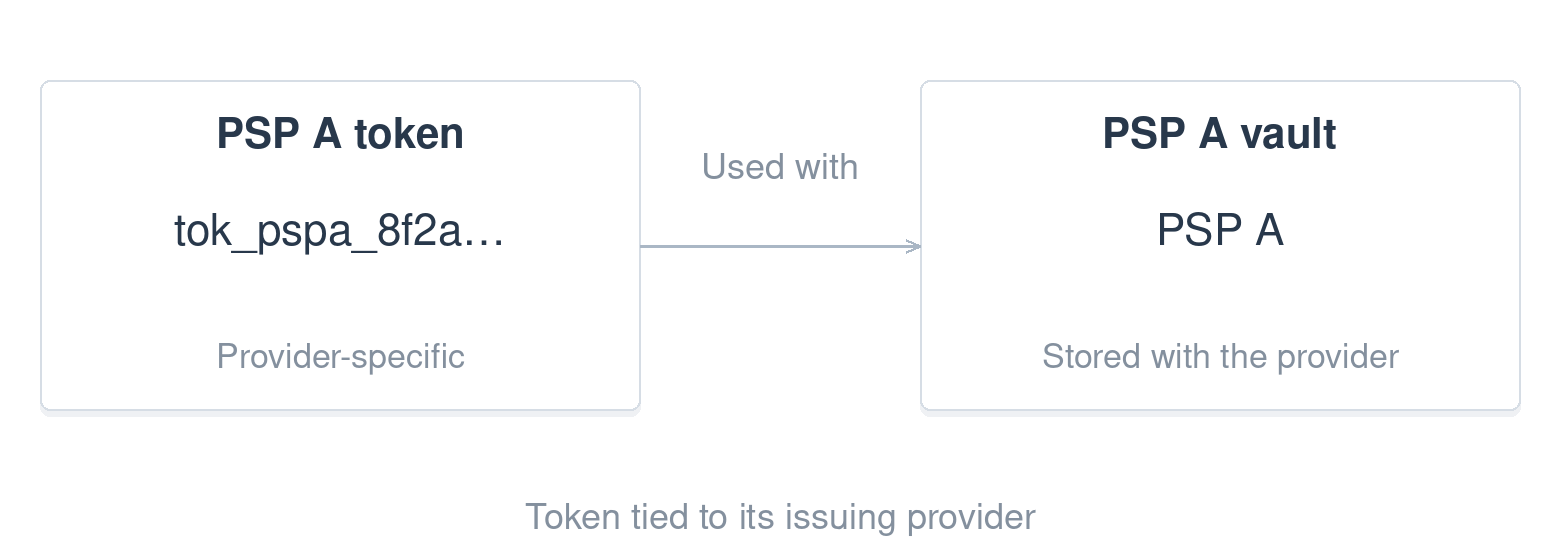
PSP vault
- Provider-issued token
- Use only with that PSP
- Available for supported integrations
Authentication
Set 3DS per transaction. We handle the path.
Enable or disable 3DS on each payment. Orchestra uses its PSP-agnostic flow by default, or the PSP’s flow where required.
| Transaction | 3DS | Execution path |
|---|---|---|
| Payment #1042 | On | Orchestra 3DS |
| Payment #1043 | Off | Not requested |
| Payment #1044 | On | PSP-required 3DS |
Security & compliance
Verified standards. Clear responsibilities.
Orchestra is PCI DSS Level 1 and ISO/IEC 27001:2022 compliant.
PCI responsibility
| Your role | PCI validation |
|---|---|
| Direct merchant | SAQ A |
| Technology provider | SAQ D for service providers |
| Platform merchant | SAQ A |
PCI scope depends on the implemented payment flow and the customer’s role.
Tokens that move with you
SaaS portfolio
Card details sit in Orchestra’s vault, independent of any processor. Moving a product to a new processor needs no re-collection from subscribers.
Ad-tech group
Switching to a new UK processor was a configuration change. Stored tokens carried over because they live in Orchestra’s vault.
Fitness software
Four PCI DSS scopes became one integration. The team used Orchestra’s 12-point PCI checklist to show its security group what it no longer had to maintain.
Build it
Capture in the browser. Get back a token.
Start a Payments Library session with CHARGE_AND_TOKENIZE. The card is captured in the browser and your server receives a token for later charges.
curl -X POST https://api.orchestrasolutions.com/EWalletOperations \
  -H "Content-Type: application/json" \
  -H "X-Api-Key: YOUR_API_KEY" \
  -d '{
    "operation": "CHARGE_AND_TOKENIZE",
    "paymentGatewayAccountId": "your-gateway-account",
    "amount": 29.00,
    "currencyCode": "EUR",
    "mode": "LIVE",
    "customerEmail": "customer@example.com",
    "merchantReference": "sub-4821"
  }'
Open a session that charges now and returns a token. From the docs.
FAQ
Questions you probably have.
How secure is Orchestra?
Security is at the heart of what we do. We abide by all the major payment compliance frameworks. By offloading security concerns to us, you’ll stay protected without compromising on ease of use.
How does tokenization storage pricing work?
Stored data is included for 3 months. After that, a monthly storage fee applies, depending on your volume. Contact sales for exact figures.
Go deeper on tokenization and PCI scope

More from the same API.
Test securely
Create a token. Use it in the sandbox.
100 live requests every month, plus unlimited sandbox testing. No credit card required.
Sandbox unlimited testing | Live 100 requests / month